October’s most consequential incidents shared one feature. The point of failure sat outside the victim’s own estate: in a cloud facility, an adviser, a vendor platform or a single engineer’s laptop. For an industry built on outsourced and shared infrastructure, that pattern deserves attention.
Private Equity is a distributed business by design. A mid-sized GP might rely on a fund administrator, a virtual data room, two or three law firms, an outsourced IT provider and a handful of SaaS platforms before it counts a single portfolio company. Each portfolio company brings its own chain of suppliers, and buy-and-build strategies stitch those chains together. That makes Private Equity cyber risk a question of connections as much as of individual companies.
Most cyber oversight in the industry still works company by company. October was a useful reminder of what that approach misses. Very little of what went wrong this month started inside the victim’s own network.
One cloud facility, several banks
On Tuesday 20 October, a power failure at a third-party facility in Google Cloud’s London region (europe-west2) disrupted services for several hours. Revolut, Lloyds and HSBC were among the banks affected. At Revolut, customers lost access to logins, card payments and cash withdrawals.
The regulatory response was quick. The European Banking Authority contacted Google, the FCA said it was engaging with the company, and the Treasury Committee wrote to the Bank of England and the FCA asking about the scale of the disruption. Reuters described the outage as the first major test of the new regimes for critical third parties: the EU designated 19 technology firms last year, and the UK has designated four cloud providers. The EBA was explicit that designation does not move responsibility away from the financial firms that depend on those providers.
Two details matter for private equity. First, the failure sat in a third-party facility used by Google, one layer beyond the provider most customers would list on a vendor register. Dependency chains run deeper than the contracts suggest.
Second, the outage hit several firms at once. That is the scenario most portfolio resilience plans are not built for. Each company’s plan assumes it is the one in trouble and that its suppliers are on hand to help. When several companies share a cloud region, a managed service provider or a payroll platform, one failure lands across the portfolio at the same time, along with the questions from lenders and LPs. Buy-and-build can sharpen the problem, because moving add-ons onto a shared platform is often part of the synergy case.
The same concentration starts at the manager level. In Thomas Murray’s Out of Sight index of 558 PE firms, published in July, the infrastructure behind the firms’ external footprint spans 52 countries, against 25 countries where the firms are headquartered. Few firms could say with confidence where all of it physically runs.
The deal perimeter includes your advisers
The second thread ran through professional services. On 28 October, Coveware, the ransomware response firm owned by Veeam, published an open letter to senior partners at law firms. It followed a leak of internal chats from the Silent Ransom Group, an extortion crew the FBI warned in May was impersonating IT staff to get into US law firms, at times by turning up in person. Coveware says the leak identified several victims that had paid to keep their incidents out of public view, and it expects most of the Am Law 100 to have been affected by the time the campaign winds down.
Separately, PwC confirmed an incident on 23 October involving a third-party vendor that hosted employee learning records, after an extortion group claimed to have taken a large volume of data. PwC said the affected site held no client data and that its own network and operations were not affected. Warp and ENGIE both disclosed breaches during the month that came through vendor or partner platforms rather than their own systems.
For deal teams, the implication is direct. During a live transaction, the most sensitive information about a target, a valuation or a financing structure often sits with counsel, accountants and data-room providers rather than with the fund. These firms are being targeted precisely because of what they hold. Asking advisers how they verify inbound IT support calls, and how quickly they would tell you about an incident, is a reasonable part of any pre-engagement checks.
One laptop, one set of keys
The month’s largest loss was at Binance. In a preliminary update after the theft on 29 October, the exchange said a compromised laptop belonging to a DevOps engineer gave the attacker access to a service that submitted unauthorised withdrawals, though it later said the attack involved additional points of breach. Binance put the impact at about $6.3bn, with around $3bn frozen, said it had found no evidence that wallet private keys were leaked, and has said it will absorb the losses itself. On 31 October the FBI attributed the theft to TraderTraitor, a North Korean state-sponsored group also tracked as Lazarus. A full technical report is still to come, and the figures may change.
Few portfolios include a crypto exchange, but the pattern is familiar. One person’s device, with broad privileged access to a payment function, was enough. In Private Equity the equivalent sits in fund treasury and capital call processes, in portfolio company finance teams, and with the administrators who can move money. It also echoes the summer, when Apollo confirmed a breach that followed a social engineering campaign Google researchers said was aimed at Private Equity and financial firms. Coveware’s third-quarter figures point the same way: phishing and social engineering were the leading route in, at around 29% of cases, with compromised credentials rising.
The mid-market is the target
Coveware’s data also says something about where attackers are aiming. The median victim in its third-quarter caseload had 1,121 employees, up 49% on the previous quarter, and the median ransom payment rose to $400,000 even as the average fell. Coveware reads this as attackers moving into the mid-market: organisations large enough to hold valuable data and capital, but often with lean security teams. That describes a large share of PE-backed companies.
There is a governance point too. Coveware reports that nearly 80% of data-theft-only incidents were resolved without a payment, and notes that paying rarely removes legal or regulatory notification duties. For a sponsor, a data extortion event at a portfolio company is therefore a board-level legal and communications decision. It is worth rehearsing before it arrives.
Regulation is catching up with the supply chain
In the UK, the Cyber Security and Resilience Bill had its Lords Report stage on 26 October, with third reading and Royal Assent still to come. As drafted, it brings managed service providers and data centres into scope. For sponsors that own IT services or MSP businesses, that points to direct statutory duties. For every other portfolio company, it means the MSP it relies on may soon be regulated, which is likely to change contracts and incident reporting.
On 20 October the ICO reprimanded Ogi Networks and Data Cymru after a ransomware attack that began with a forgotten test account protected by the password “Password1”. Basic hygiene failures, particularly in inherited or legacy accounts, still lead to enforcement. Acquired estates are full of them.
And the Google outage gave the UK critical third parties regime and the EU’s DORA oversight their first real test. Portfolio companies in financial services should expect supervisors to ask how they would have coped.
Questions for the next portfolio review
Where do portfolio companies share critical dependencies, such as a cloud region, MSP, payroll or payments provider, and has anyone assessed what happens if one fails for all of them at once?
Who holds privileged access to payment, treasury, and production systems, at the fund and in each company, and are those devices managed and monitored?
How do our deal advisers and data-room providers verify inbound IT support requests, and what have they committed to tell us, and when, if they suffer an incident?
If a portfolio company receives a data-only extortion demand, who makes the decision, and how does the response plan incorporate lenders, LPs and regulators?
Which of our businesses would fall within scope of the UK Bill, and which rely on MSPs that will?
Can we show the board and LPs a current, comparable view of cyber risk across the portfolio, rather than a set of self-assessments?
The common thread
None of the incidents above needed an attacker to defeat a well-run perimeter head-on. They went around it, through a facility, an adviser, a vendor or a person. Oversight that stops at each company’s own network will keep missing that. The firms best placed are likely to be those that map dependencies across the whole portfolio and the deal process, and test them before a provider failure forces the question.
About the Thomas Murray PE Cyber Index
The index scores 558 private equity firms on external attack surface and dark web exposure, using outside-in data only. GPs can request a confidential view of where they sit before an LP raises it, and LPs can use it to benchmark external managers. Read it here.
Sources
Reuters via The Star, Google Cloud outage (21 Oct): https://www.thestar.com.my/tech/tech-news/2026/10/21/europe039s-financial-regulators-query-google-over-cloud-outage-that-hit-banks
Coveware, Q3 2026 report and open letter (28 Oct): https://coveware.com/2026/10/the-silent-ransom-group-leak-shows-why-paying-for-silence-fails/
BleepingComputer, Silent Ransom Group and law firms (June): https://bleepingcomputer.com/news/security/silent-ransom-group-targets-law-firms-with-fake-it-support-calls
Insurance Journal, PwC incident (28 Oct): https://www.insurancejournal.com/news/national/2026/10/28/890532.htm
SOCRadar, Binance timeline (30 Oct): https://socradar.io/blog/binance-hack-6-3b-hot-wallet-theft
TechCrunch, Apollo breach (21 Aug): https://techcrunch.com/2026/08/21/private-equity-firm-apollo-confirms-data-breach-amid-hacking-wave-targeting-financial-giants/
UK Parliament, Cyber Security and Resilience Bill: https://bills.parliament.uk/bills/4035
Hill Dickinson, Bill update (15 Oct): https://www.hilldickinson.com/our-view/articles/cybersecurity-awareness-month-update-on-the-cyber-security-and-resilience-bill/
The Register, ICO reprimand (20 Oct): https://www.theregister.com/cyber-crime/2026/10/20/password1-and-a-forgotten-test-account-land-welsh-outfits-in-hot-water/5304139
Thomas Murray, Beneath the Asset: Out of Sight (July 2026), 558 firms, snapshot 15 July 2026.
- BleepingComputer, FBI attribution of Binance theft to North Korea (Nov): https://www.bleepingcomputer.com/news/security/fbi-links-63-billion-binance-crypto-heist-to-north-korean-hackers/
- Gizmodo, Binance additional points of breach: https://gizmodo.com/how-hackers-stole-6-3-billion-from-binance-in-minutes-2000833158
- CNBC, Binance covering losses and resuming withdrawals (31 Oct): https://www.cnbc.com/2026/10/31/binance-hack-asset-coverage-withdrawals.html
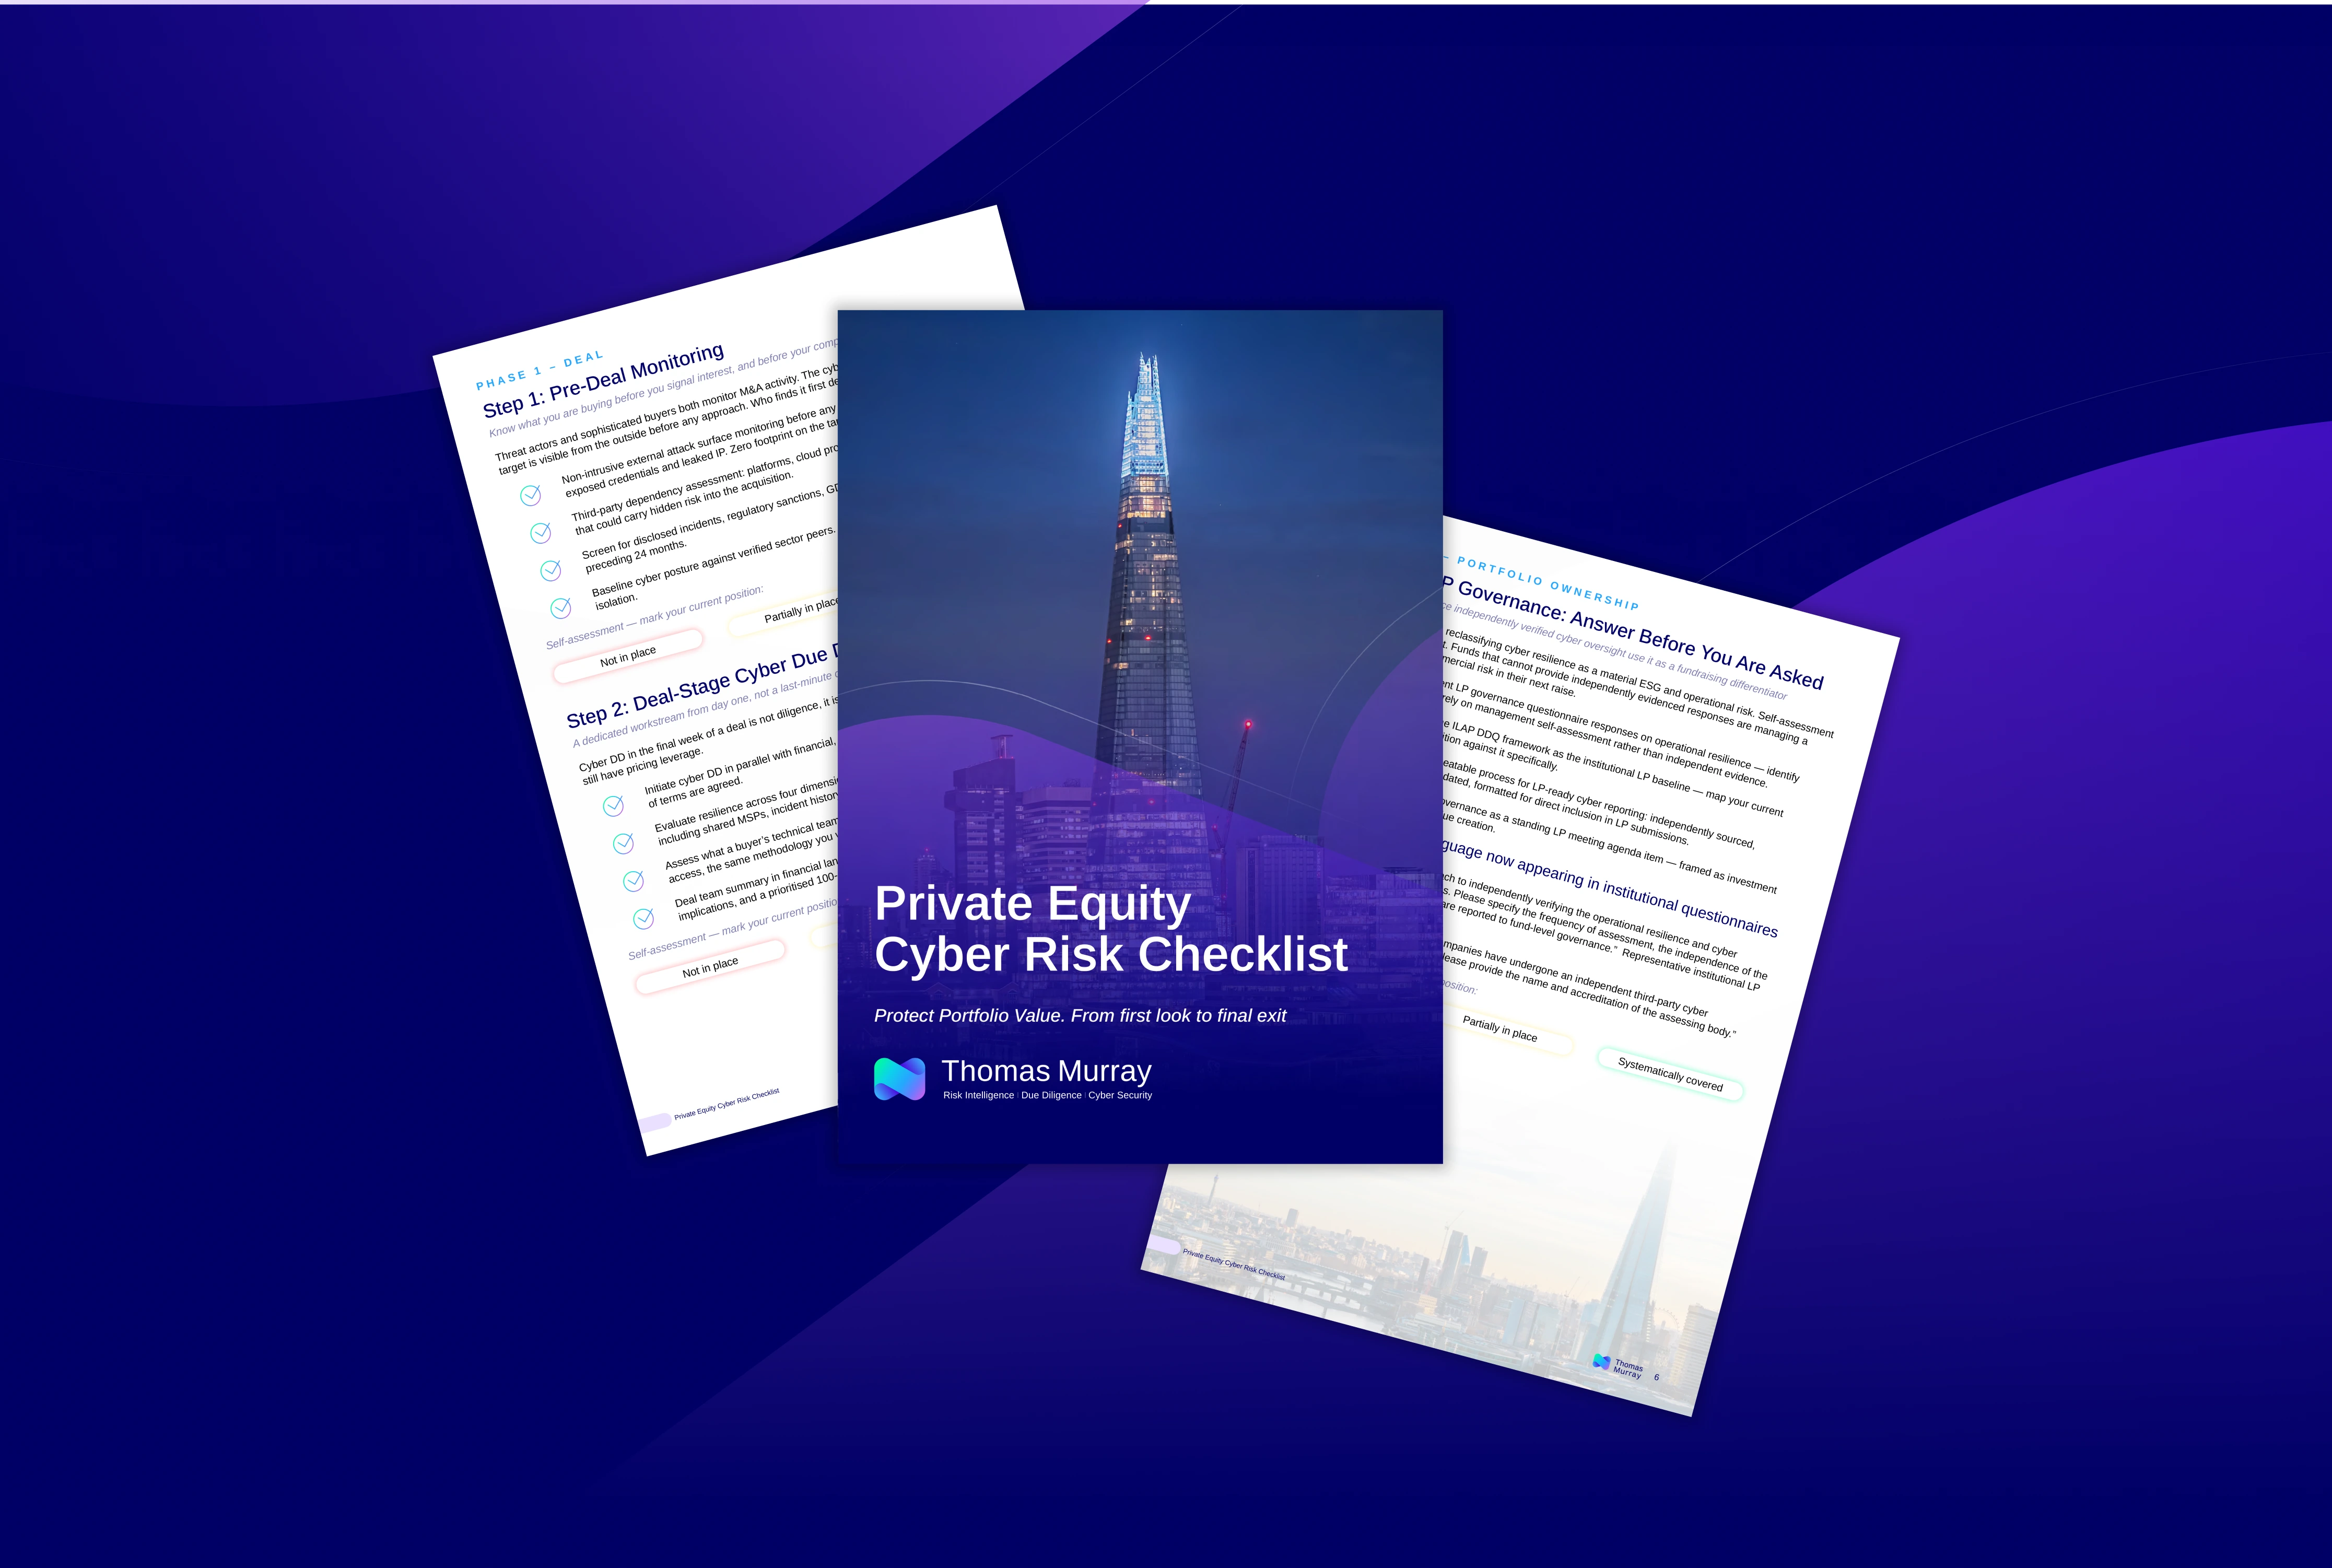
Private Equity Cyber Risk Checklist
Our PE Cyber Risk Checklist is a ten-step diagnostic for PE fund leadership, covering every stage from pre-deal surveillance to exit readiness. Work through it and know exactly where your gaps are.
- 10 steps across five phases - deal, first 100 days, portfolio ownership, ESG, and exit.
- Self-assessment at every step - rate your current position and walk away with a clear gap count.
- Written for fund leadership, No jargon. Financial language throughout.
Insights
Other People’s Networks: What October’s Cyber Incidents Mean for Private Equity
Private Equity Has a Cyber Risk Blind Spot
Private equity has become much better at assessing cyber risk, but it may be looking in the wrong place.
Beneath the Asset – Out of Sight: The State of Cybersecurity in the Private Equity Industry
The UK’s smallest investment funds are weak security link in protecting the IP needed for national growth, new Thomas Murray study finds.
Fool me once: What the Apollo breach tells private equity about the threats it now faces
Apollo’s August breach was one data point in a five-week campaign mapping 200+ private capital firms. What it means for fund-level cyber risk.